Contents
Cybersecurity has a branding problem. Open any cybersecurity company's website and you'll see the same visual language: dark backgrounds, neon accents, shields, locks, binary code, and vague promises about "protecting your digital assets." The industry that's supposed to make you feel safe often looks like it's cosplaying a movie about hackers.
This isn't just an aesthetic complaint. For cybersecurity companies, especially those selling to enterprise buyers, brand identity directly impacts trust. And trust is literally the product.
Here's why cybersecurity branding is broken and how to fix it.
The Problem: Everyone Looks the Same
Browse the websites of 20 cybersecurity startups and you'll spot the pattern instantly:
Dark navy or black backgrounds. Electric blue or green accents. A shield icon somewhere in the logo. Abstract "network" illustrations with dots and lines. Stock photos of hooded figures at keyboards. Words like "fortify," "defend," "shield," "sentinel," "guard."
This visual language made sense in 2010 when cybersecurity was a niche industry selling to IT departments. The aesthetic communicated technical sophistication to a technical audience.
But the market has changed. Today, cybersecurity products are purchased by CEOs, CFOs, board members, and compliance officers, not just CISOs. The buyers have shifted, but the branding hasn't.
When every company looks the same, differentiation disappears. A CISO evaluating five endpoint protection vendors sees five identical-looking brands and defaults to the one they've heard of, or the cheapest. Your product might be superior, but your brand isn't giving them a reason to believe that.
The industry that's supposed to make you feel safe often looks like it's cosplaying a movie about hackers.
Why Trust Needs a Different Visual Language
Cybersecurity companies sell trust. That's the core transaction: you're asking customers to believe that your product will protect their most sensitive assets.
But trust isn't communicated through shields and dark interfaces. Think about the brands you trust most in other industries: your bank, your doctor's office, your insurance provider. What do they look like?
They're clean. They're clear. They use plenty of whitespace. The typography is confident, not aggressive. The colors are calm, not alarming. They quietly communicate competence instead of screaming "DANGER!"
That's the gap. Cybersecurity brands are designing for drama when they should be designing for confidence.
Five Principles for Cybersecurity Brand Identity
1. Choose Calm Over Aggressive
The instinct in cybersecurity branding is to look tough. Dark colors, sharp angles, military metaphors. But aggressive aesthetics trigger anxiety, not confidence.
Consider the difference between a hospital emergency room and a doctor's private practice. Both deal with health, but one signals urgency and crisis, the other signals expertise and care. Your cybersecurity brand should feel like the private practice: competent, calm, in control.
In practice, this means: lighter color palettes (not necessarily white, but not perpetual dark mode), rounded typography rather than angular, and imagery that suggests stability rather than warfare.
2. Simplify Your Visual Language
Complexity communicates confusion rather than sophistication. The most trusted brands in any industry are visually simple.
Drop the abstract network illustrations. Drop the binary code backgrounds. Drop the glowing orbs and floating shields. Replace them with clean typography, structured layouts, and purposeful use of space.
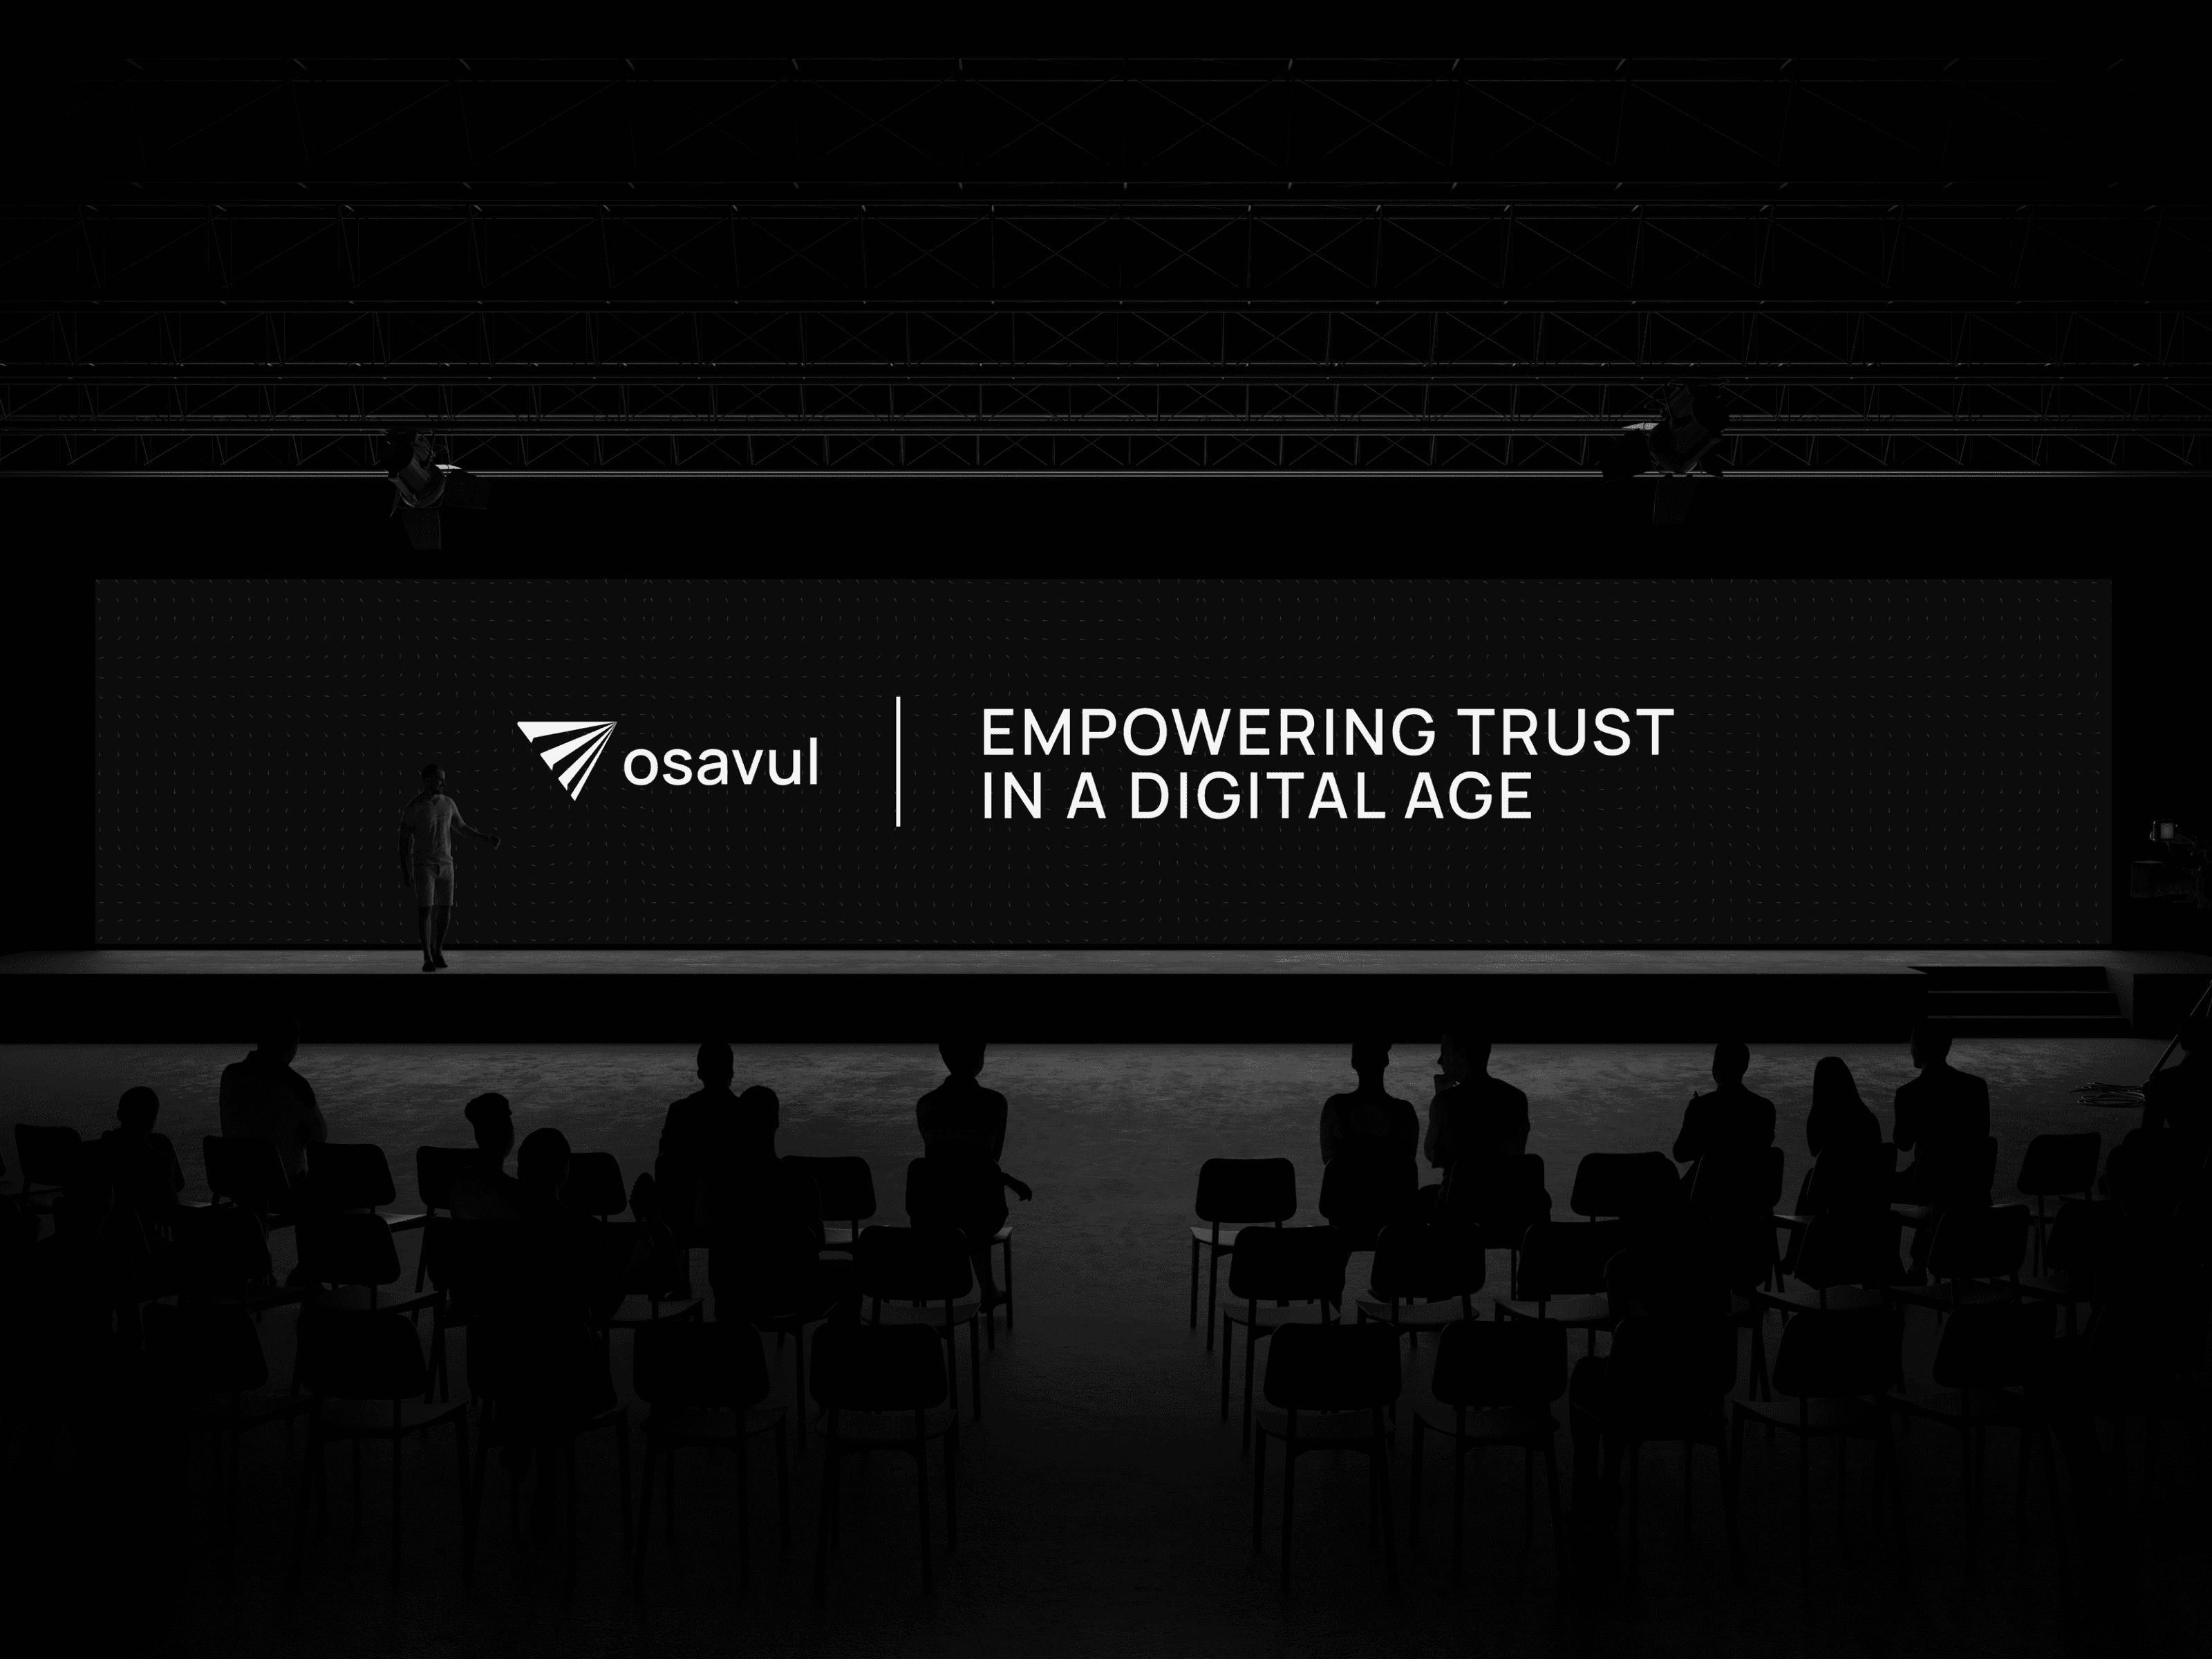
Our identity for Osavul, an AI-driven cybersecurity company, is built on this principle. The task was a sharp, minimal identity that reads as intelligent and precise. We designed a logo of converging lines, which stand for scattered data turning into usable insight, a monochrome palette, and a structured brand system that holds it all together.
3. Build Credibility Through Structure, Not Decoration
Enterprise buyers evaluate brands subconsciously. A well-structured, consistent brand signals a well-structured, reliable company. A messy, inconsistent brand signals the opposite.
This means your brand system needs to be rigorous:
- Consistent typography across every touchpoint: website, pitch deck, product UI, email signatures
- A defined grid system for layouts
- Clear hierarchy in information design
- Brand guidelines that your whole team actually follows
Decorated brands feel amateur. Structured brands feel trustworthy. In cybersecurity, the difference between the two can cost you a seven-figure deal.
4. Differentiate Through Personality, Not Gimmicks
If you can't use shields, locks, and dark themes, how do you signal "cybersecurity"?
You don't need to signal the category. You need to signal your specific position within it.
Are you the enterprise-grade platform for regulated industries? Your brand should feel institutional and precise. Are you the developer-first security tool? Your brand should feel technical but approachable. Are you the AI-powered threat detection startup? Your brand should feel intelligent and forward-looking.
The personality comes from your positioning, not from industry clichés. When you know who you are and who you're for, the visual language follows naturally. This is why brand strategy needs to come before brand identity.
5. Design for the Actual Buyer
A CISO might evaluate your product, but the purchase decision often involves a CFO, a CTO, a compliance officer, and sometimes the board. Your brand needs to resonate with all of them.
What does this mean practically?
- Your website shouldn't feel like a hacker's terminal. It should feel like a trustworthy business partner.
- Your pitch deck shouldn't rely on fear. It should present data, outcomes, and clarity.
- Your product documentation should be clean and readable, not stuffed with jargon and dark-themed code blocks.
- Your social media presence should demonstrate thought leadership, not just repost threat alerts.
The companies winning in cybersecurity branding right now (CrowdStrike, Wiz, Snyk) have figured this out. Their brands feel like technology companies, not spy movies.
Case Study: How It Works in Practice
When we worked with Osavul, an AI-driven cybersecurity company, the brief called for a sharp, minimal identity that communicates intelligence, precision, and trust and stays consistent across platforms.
The project covered brand identity, brand guidelines, and logo design. What we made:
- A logo built from converging lines, symbolizing scattered data turning into actionable insight
- A monochrome color palette for clarity, precision, and focus
- A structured brand system with rules for typography, layout, and applications
- A brandbook that keeps the identity consistent across digital, print, and product communication
The logo, palette, and brandbook are shown in the full Osavul case study.
What to Include in Your Cybersecurity Brand System
If you're building or rebuilding a cybersecurity brand, here's what your identity system should cover. For a detailed breakdown of each element, see our brand identity checklist.
Logo system: A mark that works at every size, from website header to app icon to conference badge. Avoid shields, locks, and generic security symbols. Your logo should be yours, not a category cliché.
Color palette: Move away from the dark-blue-and-neon default. Consider colors that signal confidence and clarity: deep greens, warm neutrals, sophisticated grays. Whatever you choose, ensure strong contrast ratios for accessibility.
Typography: Choose typefaces that feel authoritative without being aggressive. Geometric sans-serifs work well for cybersecurity: they feel precise and technical without the cyberpunk baggage. Avoid monospace fonts for brand typography (save them for actual code).
Visual system: Define how illustrations, diagrams, and data visualizations should look. Cybersecurity products often need to explain complex concepts, and your visual system should make those explanations clear, not more confusing.
Tone of voice: Cybersecurity copy tends toward fear-based messaging ("threats are everywhere, you're vulnerable, buy our product"). The brands winning enterprise deals use a different approach: informed authority. They educate rather than alarm.
FAQ
Does cybersecurity branding really affect sales?
Yes. Enterprise buyers evaluate trust signals at every touchpoint. A professional, consistent brand reduces perceived risk, which is exactly what a cybersecurity company should be doing.
Can I rebrand without confusing existing customers?
Absolutely. A rebrand doesn't mean changing everything overnight. It means evolving your visual system to better represent your current positioning. Most cybersecurity rebrands retain core brand elements (name, key colors) while upgrading the system around them.
How is cybersecurity branding different from other B2B tech branding?
The trust stakes are higher. A project management tool can get away with a playful brand. A cybersecurity product that looks playful signals "we don't take security seriously." The balance is between being approachable and being credible, and credibility must win.
Should I hire an agency that specializes in cybersecurity?
Not necessarily. What you need is an agency that understands B2B tech and can think strategically about positioning. Deep cybersecurity knowledge helps, but design thinking and brand strategy matter more. An agency that knows how to build trust through design will produce better work than one that just knows the cybersecurity market but designs like everyone else in it.
Conclusion
Cybersecurity branding is stuck in a loop: dark backgrounds, shields, neon accents, fear-based messaging. The companies that break out of this pattern and design for trust instead of drama will win the next generation of enterprise buyers.
Your product protects sensitive data and critical infrastructure. Your brand should communicate that with the same level of care, precision, and confidence.
If you're building a cybersecurity company and your brand still looks like every other vendor in the space, let's talk about changing that.